Category: Cyber Attacks & Threat Trends

Water Utilities Have a Cybersecurity Problem, and It’s Not a Lack of Frameworks
A few weeks ago, I wrote that AWIA was never enough to address the cybersecurity risks facing U.S. water utilities. Since then, we’ve gotten another reminder of why. In late July, the FBI and EPA warned that attackers had targeted internet-facing PLCs at water and wastewater utilities across multiple states, in some cases causing operational… Read more »
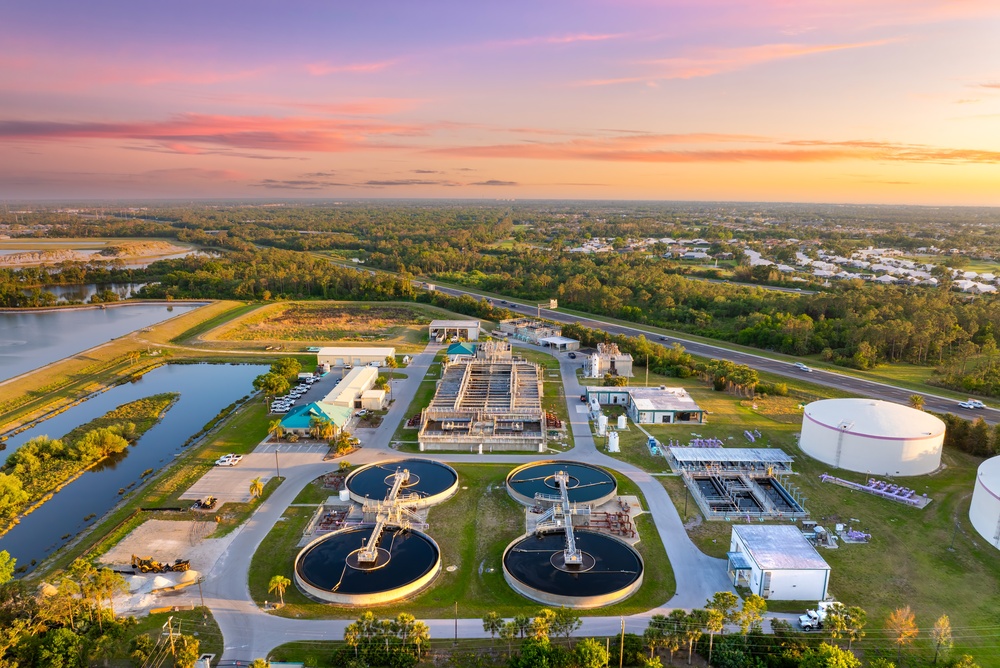
AWIA Was Never Enough. The Latest Water Utility Attacks Prove It.

The cyberattacks against water utilities reported over the past week have generated a familiar response. Questions about attribution. Discussions about foreign adversaries. Renewed calls for additional funding. And, inevitably, renewed conversations about compliance. Those conversations miss the point. Whether these attacks ultimately trace back to Iranian actors or another threat group is important for national… Read more »

The Fairlife Attack Shows Why Manufacturers Can’t Afford to Guess

Over the past several weeks, the cyberattack against Coca-Cola’s Fairlife dairy business has continued to evolve. On July 16, Coca-Cola disclosed that Fairlife had experienced a ransomware event involving unauthorized access to a portion of its systems, including production-related systems, prompting the company to temporarily suspend U.S. production. Days later, ransomware group Anubis claimed responsibility… Read more »

Critical Alert: Microsoft SharePoint Zero-Day Exploited in Active Attacks (CVE-2025-53770)

Unpatched SharePoint? This Zero-Day Could Let Attackers In Microsoft has issued an urgent warning regarding a newly weaponized zero-day vulnerability, CVE-2025-53770, affecting on-premise SharePoint Server deployments. With a CVSS score of 9.8, this remote code execution (RCE) flaw is being actively exploited and poses a severe risk to unpatched environments. What’s the Threat? This unauthenticated… Read more »

Response to CrowdStrike Falcon Sensor Agent Issue Affecting Microsoft Devices

As of 0409 UTC, a critical issue with CrowdStrike Falcon Sensor agents on Windows devices has caused significant global outages. This was not a security incident or cyberattack, and DirectDefense’s infrastructure was not affected by this outage. The root cause has been identified as an automatic content deployment applied to Windows hosts, which has resulted in… Read more »

Tales From the Road: Minimize Third-Party Software Security Risks

How to Prevent Credential Stuffing with IPv6 Protocol Security Third-party software security risks are created when third-party vendor products lack security, giving attackers wide open access to your organization’s networks and databases. When a vendor has access to your network, including customer and corporate information, your own company’s security doesn’t cover all the gaps, so… Read more »